Hunting BloodHound-Style Attack Paths
Learn to map and hunt AD attack paths the way BloodHound does before an attacker finds the shortest route to Domain Admin.
Learn to map and hunt AD attack paths the way BloodHound does before an attacker finds the shortest route to Domain Admin.
A working guide to hunting AD attacks Kerberoasting, DCSync, golden tickets, and the log sources that actually catch them.
A practical guide to hunting credential theft across LSASS, SAM, DPAPI, and cached secrets on Windows before attackers cash them in.
Registry run keys are just the beginning. A systematic guide to hunting every persistence mechanism attackers use to survive a reboot on Windows.
No file, no hash, no signature to match. Here's how threat hunters actually find fileless malware and injected code living purely in memory.
Attackers use legitimate Windows binaries to blend in with normal admin activity. Here's how to hunt LOLBAS abuse without drowning in false positives.
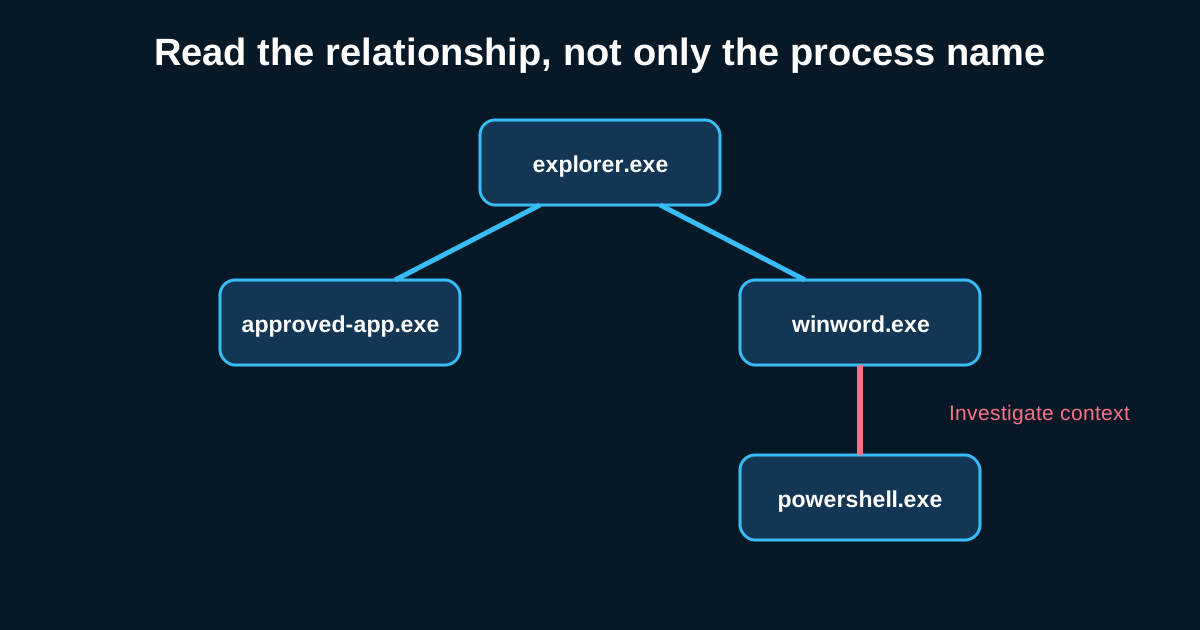
Parent-child process relationships tell the real story of an attack. Here's how to read Windows process trees like a threat hunter.
A practical capstone walkthrough for building an end-to-end detection pipeline from Sigma rule to version control to live SIEM deployment.
YARA rules let hunters detect malware families and attacker tooling by pattern, not just hash. Here's how to write ones that actually hold up.
Sigma is the closest thing threat hunters have to a universal rule language. Here's how to write Sigma detections that actually translate cleanly.