Purple Teaming Fundamentals Bridging Red and Blue
Purple teaming turns red team findings into faster detection engineering cycles. Here's how to run one that actually improves coverage.
Purple teaming turns red team findings into faster detection engineering cycles. Here's how to run one that actually improves coverage.
Apply version control, testing, and CI/CD to detection rule management. A practical look at detection-as-code for SOC teams.
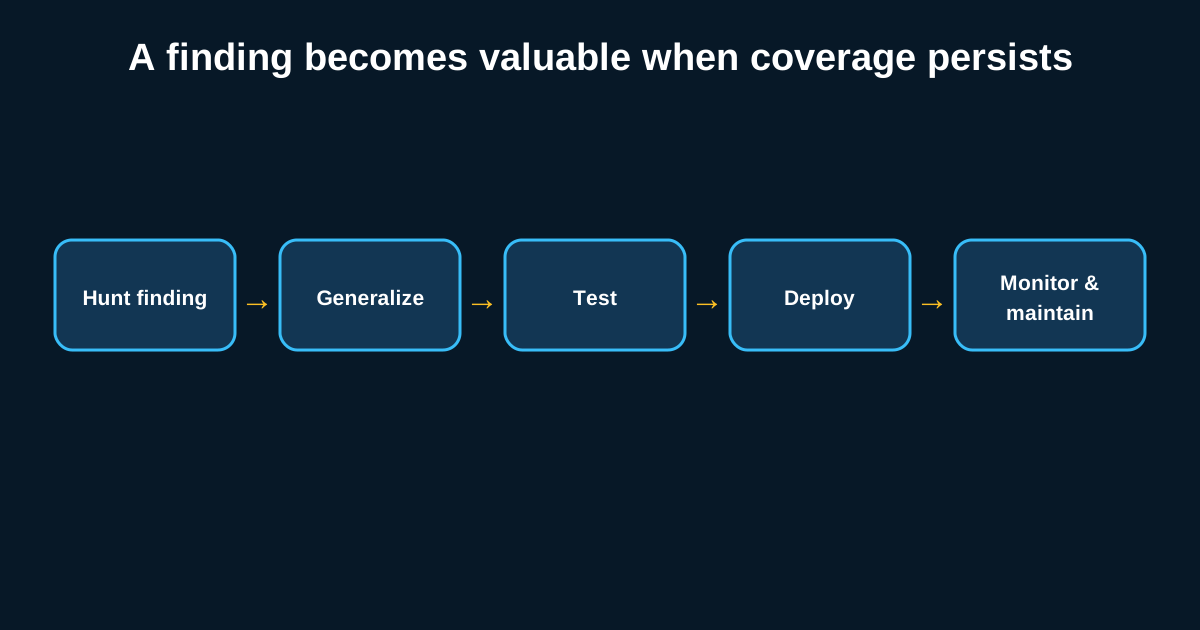
Learn how detection engineering turns one-off threat hunting findings into durable, tuned detections your SOC can trust.
Run a complete cloud hunt against a simulated credential-based breach the capstone that ties identity, API, and network layers together.
Serverless functions and IaC templates create attack surfaces most hunting programs haven't caught up to yet. Here's where to start.
Containers live for minutes, not months. Here's how to build real threat hunting capability across container and Kubernetes environments.
Stolen cloud credentials move differently than an on-prem attacker. Here's how to hunt lateral movement across AWS, Azure, and GCP.
M365 gets all the hunting attention. Here's how to extend the same discipline to Salesforce, Workday, and other business-critical SaaS.
M365 compromise rarely stays in one app. Here's how to hunt across Exchange, SharePoint, and Teams using Unified Audit Log data.
Okta sits at the center of the attack surface for thousands of orgs. Here's how to hunt System Log events for compromise and abuse.