Hunting Execution: PowerShell and Living-Off-the-Land Binaries
A focused, practical guide to hunting PowerShell abuse and living-off-the-land binaries, the execution techniques attackers rely on most.
A focused, practical guide to hunting PowerShell abuse and living-off-the-land binaries, the execution techniques attackers rely on most.
A hunter's guide to detecting execution techniques used after initial access, from scripting interpreters to scheduled task abuse.
Detecting initial access through supply chain compromise and abuse of trusted third-party access, the hardest foothold to hunt for.
How to hunt for the techniques adversaries use to gain their first foothold, before it turns into a deeper compromise.
How to hunt for adversary infrastructure being staged and developed, catching signals of an attack before it's actually launched.
Hunt external scanning, enumeration, and social-engineering preparation as early-warning signals before an intrusion.
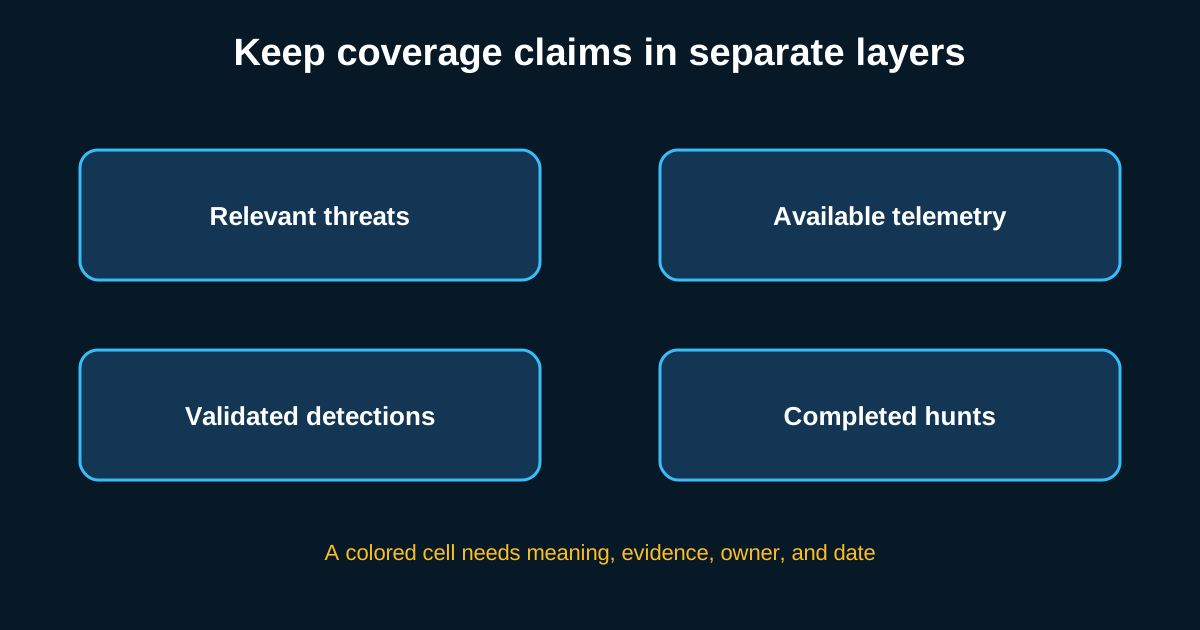
Mastering MITRE ATT&CK Navigator as a real hunt planning and documentation tool, not just a reference chart on the wall.
A capstone exercise running three full end-to-end threat hunts using intelligence-driven, behavioural, and TTP-based methodologies.
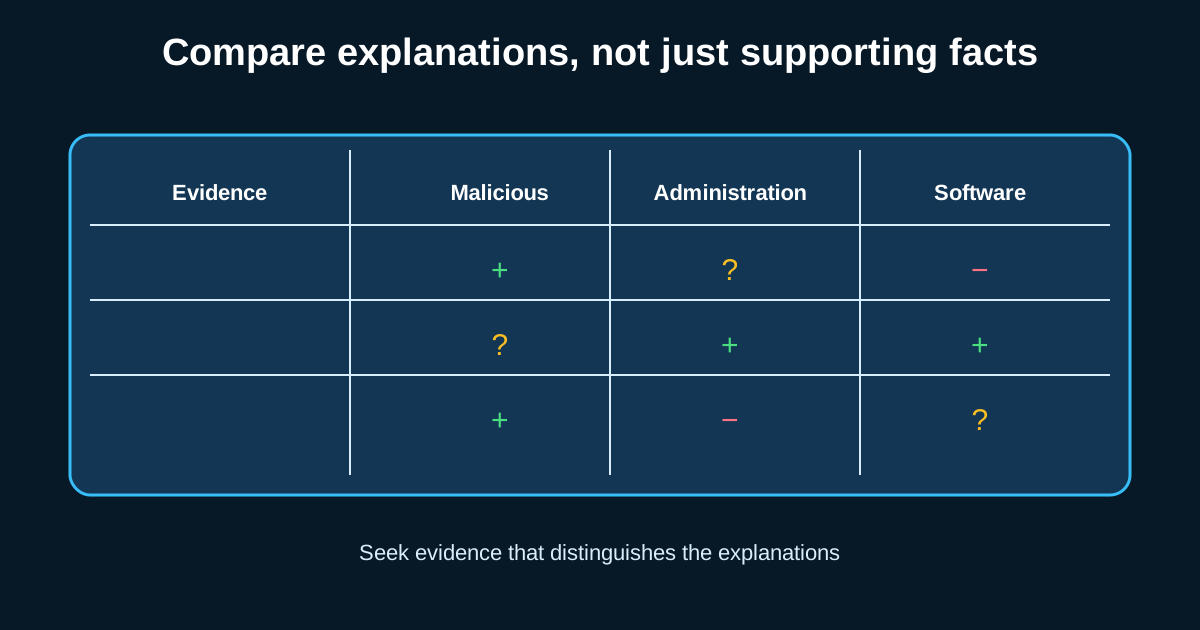
How intelligence analysis methods like ACH and devil's advocacy help hunters catch their own cognitive bias before it costs an investigation.
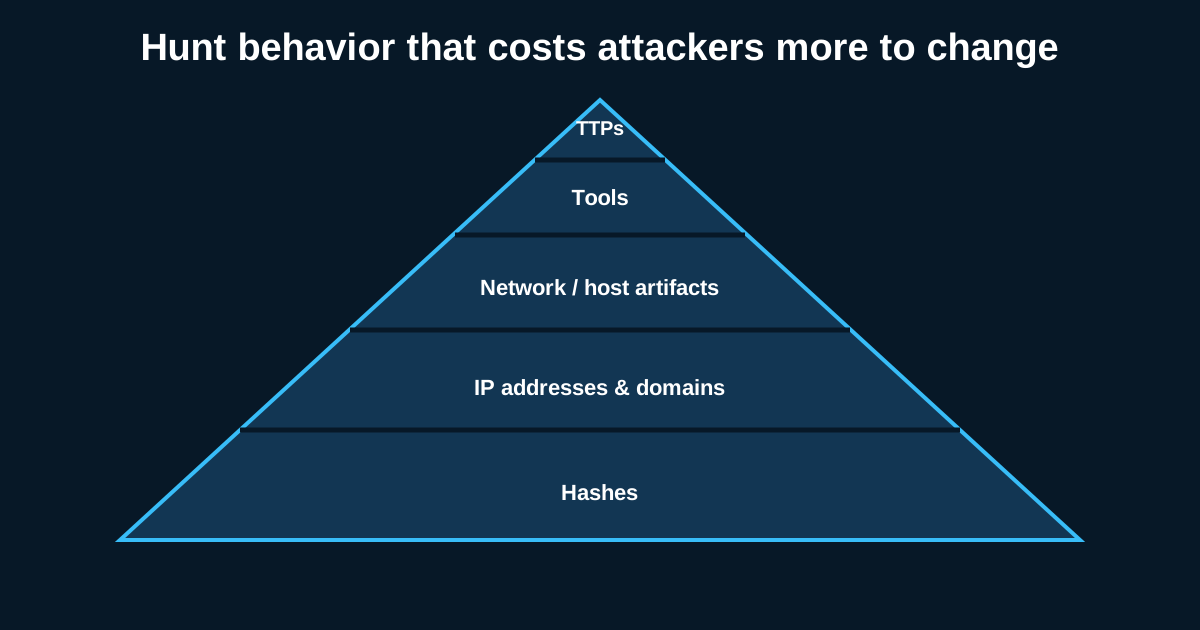
Why hunting attacker tactics, techniques, and procedures instead of artefacts produces the most durable, hardest-to-evade detections.