Hunting Lateral Movement: Following Attackers Across Your Network
A complete guide to detecting the techniques attackers use to move between hosts once they're established inside your network.
A complete guide to detecting the techniques attackers use to move between hosts once they're established inside your network.
Detecting the reconnaissance and enumeration techniques attackers use after initial access, before deciding where to move next.
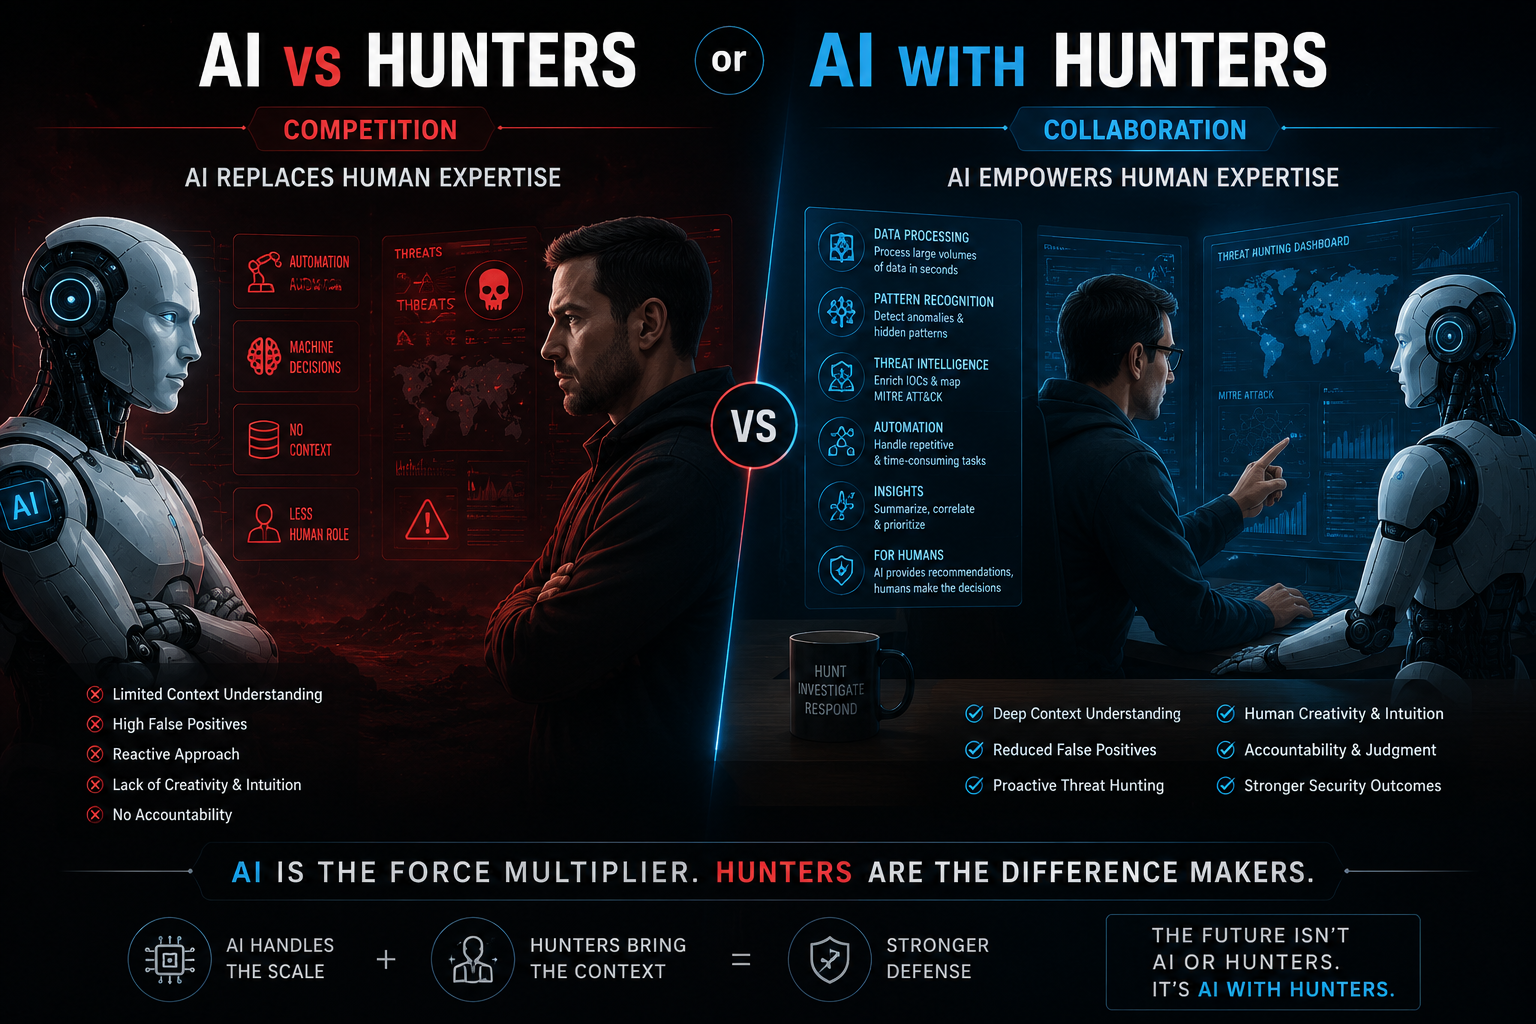
AI will transform how threat hunters work, but it cannot replace the human judgment, intuition, creativity, business context, and decision-making that make threat hunting effective.
A deep dive into hunting Golden Ticket, Silver Ticket, and AS-REP roasting attacks against Kerberos authentication in Active Directory.
A complete guide to detecting the methods attackers use to steal credentials from Windows systems, from LSASS dumping to Kerberoasting.
A deep dive into detecting process injection and hollowing, the evasion technique underpinning much of modern malicious tradecraft.
Why defense evasion is the hardest ATT&CK tactic to detect, and how hunters should approach techniques built specifically to defeat them.
How to detect the techniques attackers use to escalate from a standard user account to administrator or SYSTEM-level access.
A focused, practical deep dive into hunting the three most common Windows persistence locations attackers actually rely on.
A complete guide to hunting the persistence mechanisms attackers rely on to maintain access across reboots, credential changes, and time.