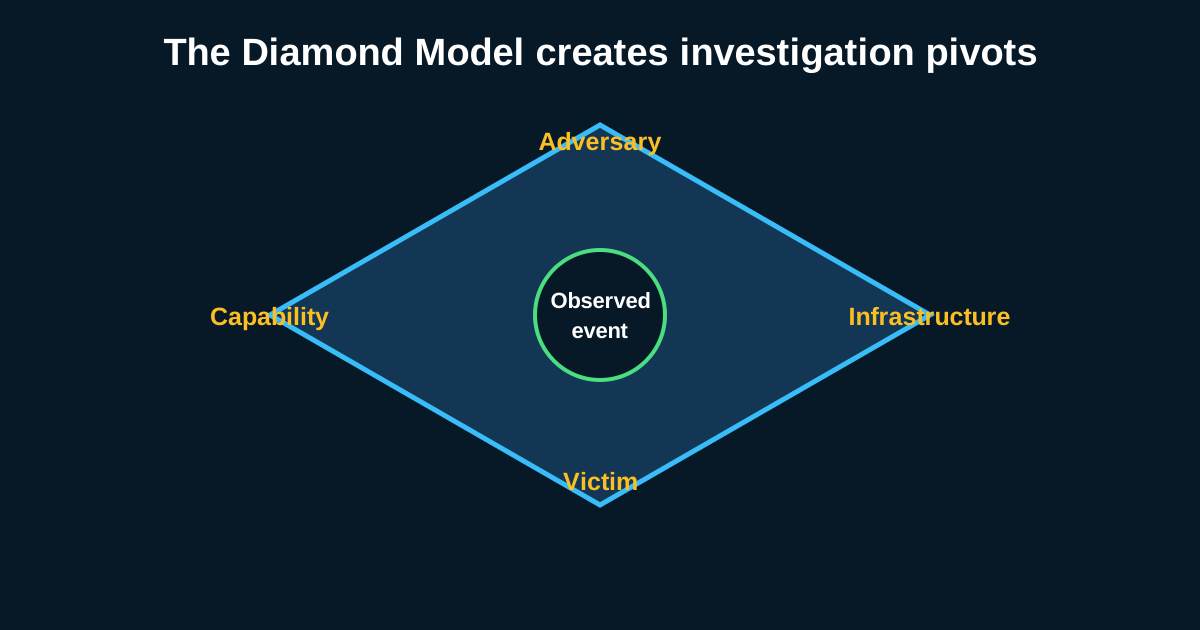
The Diamond Model: Give Your Hunts Structure
Applying the Diamond Model of intrusion analysis to enrich hunt hypotheses with actor, capability, infrastructure, and victim context.
Applying the Diamond Model of intrusion analysis to enrich hunt hypotheses with actor, capability, infrastructure, and victim context.
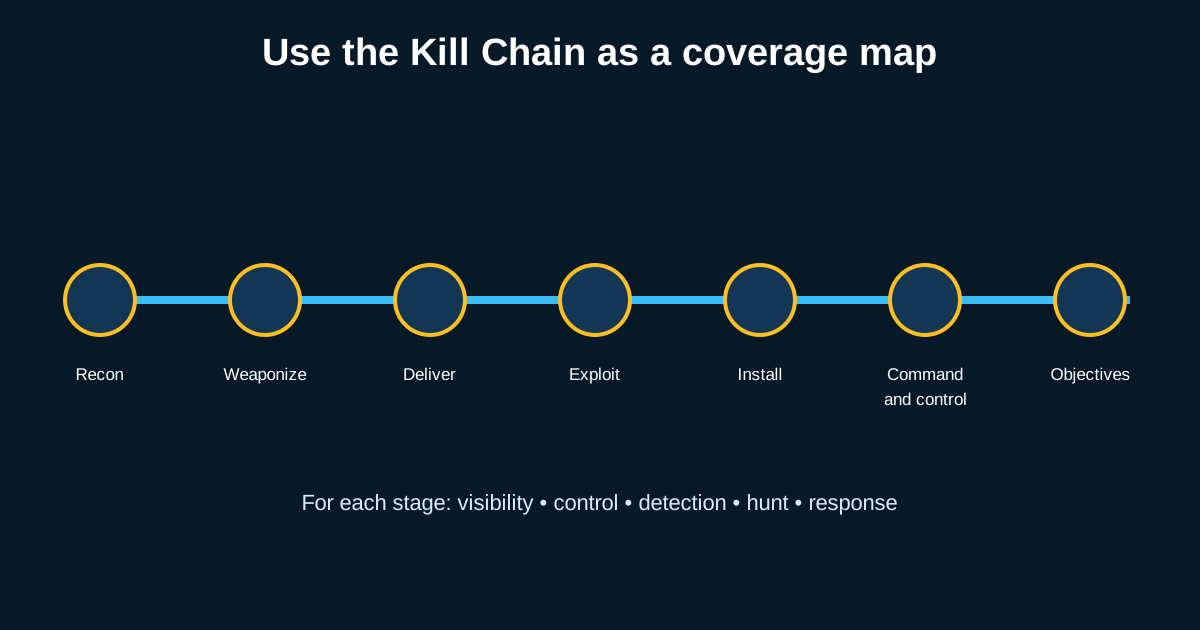
Using the cyber kill chain model to identify where hunting opportunities actually exist at each stage of an intrusion.
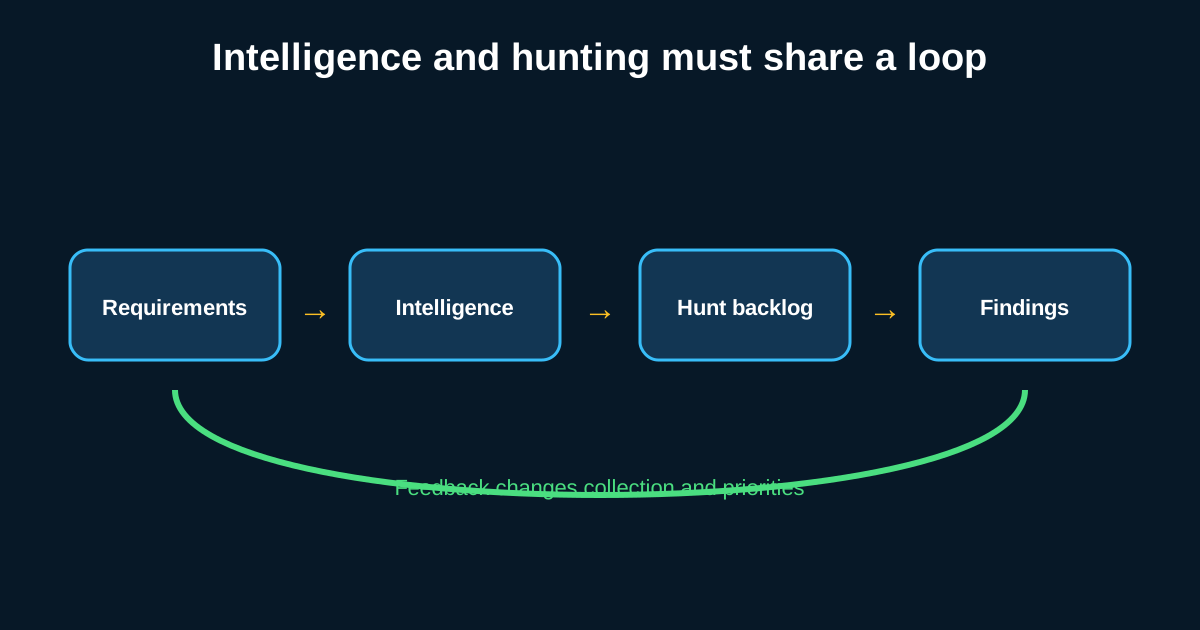
How to design a CTI function that continuously produces testable hunt hypotheses, instead of a report archive nobody reads.
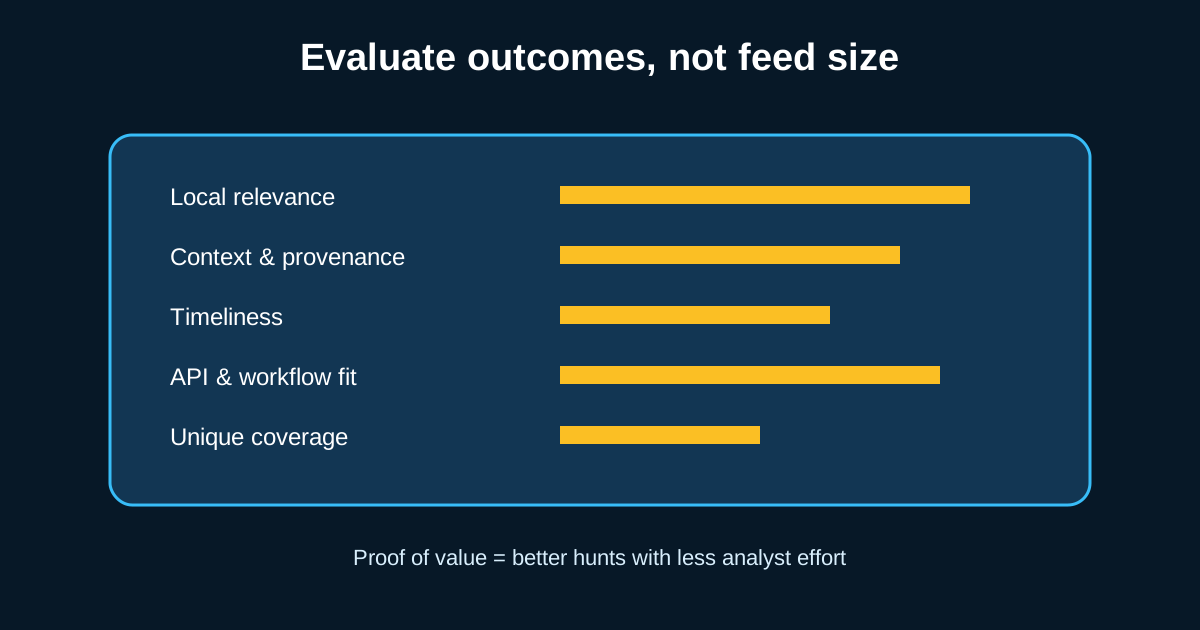
How to evaluate commercial threat intelligence platforms as a hunter, and what actually separates hunt-useful CTI from an expensive feed.
A practical guide to evaluating open-source threat intelligence and turning it into testable hunting hypotheses.
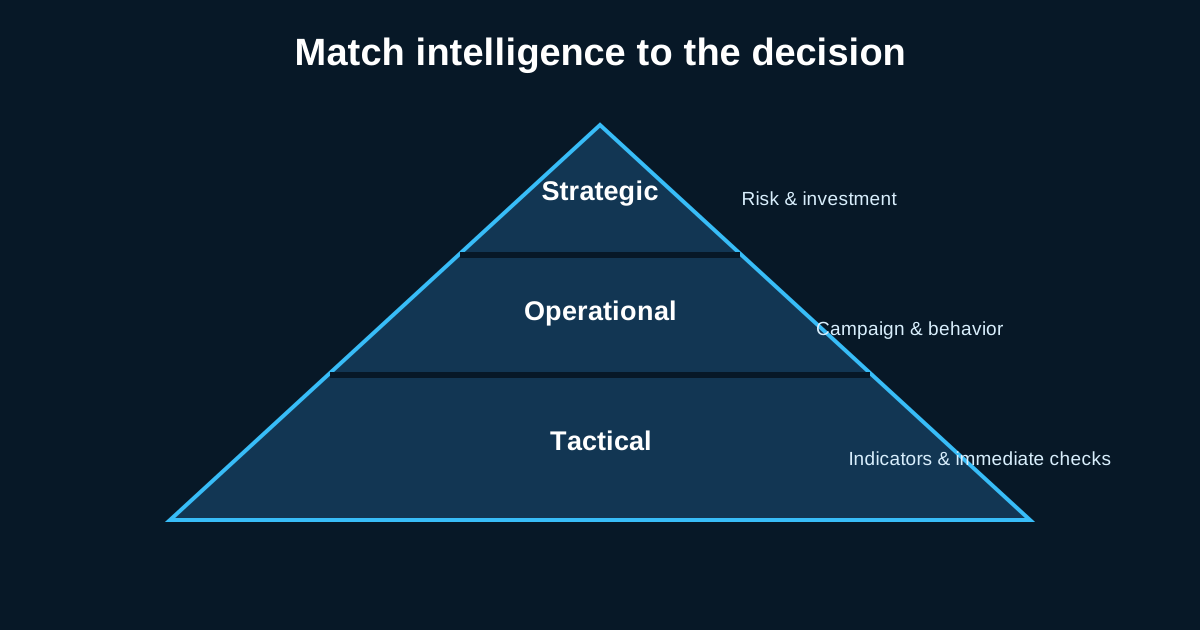
A hunter's guide to the three levels of cyber threat intelligence and exactly how each one should shape a different kind of hunt.
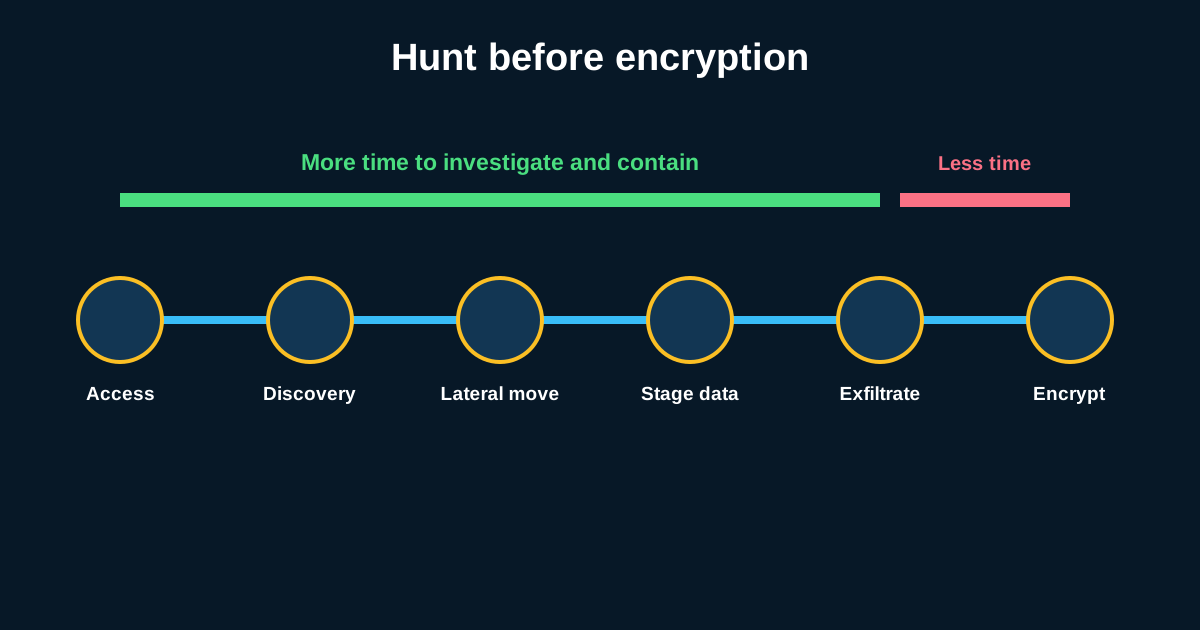
Understanding ransomware-as-a-service operations phase by phase, and where each stage gives a hunter a real chance to catch it early.
How to study documented APT campaigns and extract genuinely hunt-relevant intelligence, instead of just admiring the sophistication.
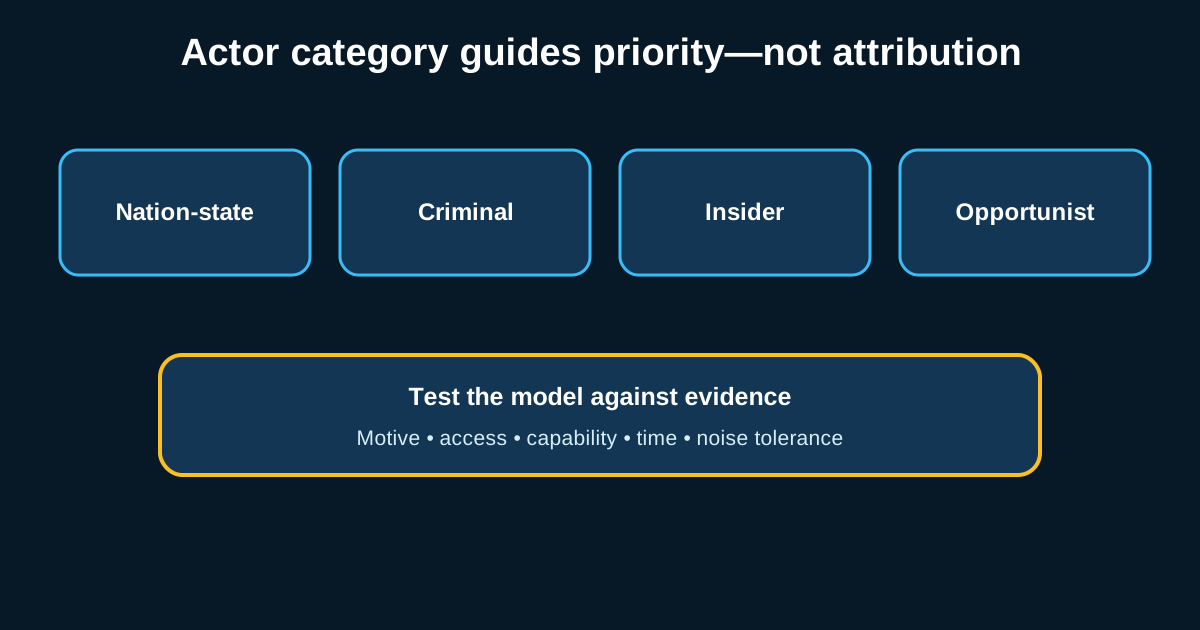
A hunter's guide to nation-state, criminal, insider, hacktivist, and opportunistic threats—and how actor intent shapes a hunt.
A capstone exercise that turns foundational threat-hunting knowledge into an operational program design.